The latest Linux Foundation CKAD test braindump guarantee a high score
TestBraindump provide you with CKAD braindump latest and CKAD test questions, which are created by our extraordinary teammates who study the CKAD braindump actual test for a long time. And we always check the update of the CKAD test braindump, the system will send you the latest version of Linux Foundation CKAD real braindump once there is latest version released. So you can trust us about the profession and accuracy of our CKAD test braindump. If you still doubt our ability, you can download the free trial of CKAD braindump Linux Foundation Certified Kubernetes Application Developer Exam study materials before you buy. If you decide to join us, you just need to send one or two days to practice CKAD test questions and remember the key knowledge of the test. I think if you practice our CKAD test braindump skillfully, you will pass the test easily.

Different versions according to your study habits
The version of Pdf is suitable to most common people because it can be print out and is easy to read. And you can share with other people about CKAD test braindump anytime.
The version of test engine is a simulation of the CKAD braindump actual test, you can feel the atmosphere of Linux Foundation CKAD test exam and get used to the condition of the real test in advance. It only can support the Windows operating system. In the course of CKAD test exam, you will know your shortcoming and strength well.
The version of online test engine just same like test engine. But it can download CKAD test braindump study materials in any electronic equipment, such as: Windows/Mac/Android/iOS operating systems. The online version is only service you can enjoy from our TestBraindump. The most advantage of online version is that you can practice CKAD test questions anytime and anywhere even if you are unable to access to the internet. So you can do CKAD real braindump in the bus or waiting someone. You can learn anywhere.
The benefit of Obtaining the CNCF Certified Kubernetes Application Developer
Those who pass the CNCF Certified Kubernetes Application Developer Exam with the help of CNCF CKAD Dumps gain several benefits:
- You might be eligible for a higher salary.
- CNCF Certified Kubernetes Application Developer tells employers that you have the knowledge they need to do the job.
- It will help employers assess how qualified candidates are for their job requirements.
- The CNCF Certified Kubernetes Application Developer allows you to work on the projects that you create.
- This certification will provide you with a good foundation for the Oracle Certified Associate Cloud + Container Administrator exam.
- This certification will help you get a job in the Kubernetes space.
- CNCF Certified Kubernetes Application Developer is recognized by many DevOps organizations.
How can you stand out from thousands of candidates? How can you make your employer think highly of you? How can you qualify for the promotion? Passing CKAD test exam will make these dreams come true. As an important test of Linux Foundation, CKAD test exam become popular among people. The considerable salary and decent work and different kind benefits, the chance of training, all these stuff attract to you. Passing CKAD braindump actual test is a new start for you. But it is a tough task. You have to sacrifice your rest time to practice the CKAD test questions and learn CKAD braindump study materials. And the worst result is that you maybe fail the exam, it will be a great loss of time and money for you. In case this terrible thing happens, TestBraindump will be your best partner to help you pass CKAD test exam.
What is the cost of CNCF Certified Kubernetes Application Developer
- Length of Examination: 120 minutes
- Format: Multiple choices, multiple answers
- Cost: $300 USD
- Passing score: 70%
- Number of Questions: 40
Reference: https://training.linuxfoundation.org/certification/certified-kubernetes-application-developer-ckad/
The service of TestBraindump
Update Our Company checks the update every day. If you've bought CKAD test braindump from us, once there is the latest CKAD - Linux Foundation Certified Kubernetes Application Developer Exam exam version, our system will send it to your e-mail automatically and immediately. And you can free update the Linux Foundation CKAD braindump study materials one-year if you purchase.
Refund We promise to you full refund if you failed the exam with CKAD test braindump. Within 7 days after exam transcripts come out, then scanning the transcripts, add it to the emails as attachments and sent to us. After confirmation, we will refund immediately.
Discount We will offer you different discount for you if you became a member of us.
Payment Our payment is by Credit Card. But it can be bound with the credit card, so the credit card is also available.
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
What languages and platforms do it work with?
Kubernetes supports programming languages such as C++, Go, Java, Python, and PHP. All of them can be used on both Mac and Linux. Week runtime. runtime. There are various container orchestration frameworks available, but Kubernetes is unique because of its versatility. Search and discover applications developed in other languages and run them anywhere. The button shows you the price in your native currency. Saves costs by reducing unnecessary resource utilization. African diaspora, and other digital immigrants. You can quickly test your applications in multiple environments. Provides a very good platform for testing. In addition to Python and Java, Python 3 is supported by Kubernetes. Attempts to raise the level of security. Avoid vulnerabilities and infection by attackers. You can run Kubernetes in a variety of environments, such as cloud providers, bare metal, and virtual machines. Avoid the configuration overhead. Containers have a specific IP address that is different from the location of the underlying physical machine. CNCF CKAD Dumps can help you achieve that.
What is the difference between Kubernetes and OpenStack?
OpenStack is a service-oriented cloud computing platform. It is massive and complex. You can't use it to develop multi-container applications. It enables multiple users to access a cloud platform. OpenStack is a framework that can be used by many different cloud providers. You can install it on your own infrastructure or any cloud provider. Windows support is not available but Linux and macOS are supported. You can use it with IaaS or PaaS providers. Allows you to create private clouds with different authentication methods and storage options. Kubernetes provides a lot of additional configuration options. Cluster size is limited and can't be changed. You must deploy all your applications and then adjust each application's requirements. Not that easy to use, and you need to know a lot of details about it. Concepts are different from Kubernetes. You can use it if you have no programming skills or Linux knowledge. Absolutely necessary for implementing Kubernetes. It is scalable. Good support for written documentation. Great support for developing open-source software.
Linux Foundation CKAD Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Application Observability and Maintenance | 15% | - Debugging in Kubernetes - Utilize container logs - Implement probes and health checks - Use built-in CLI tools to monitor Kubernetes applications - Understand API deprecation policies |
| Application Deployment | 20% | - Use the Helm package manager to deploy existing packages - Use Kubernetes primitives to implement common deployment strategies (e.g., blue/green or canary) - Kustomize - Understand Deployments and how to perform rolling updates |
| Application Environment, Configuration and Security | 25% | - Understand authentication, authorization and admission control - SecurityContexts - Discover and use resources that extend Kubernetes (CRD, Operators) - Understanding and defining resource requirements, limits and quotas - ConfigMaps and Secrets - ServiceAccounts |
| Application Design and Build | 20% | - Utilize persistent and ephemeral volumes - Choose and use the right workload resource (Deployment, DaemonSet, CronJob, etc.) - Define, build and modify container images - Understand multi-container Pod design patterns (e.g., sidecar, init and others) |
| Services and Networking | 20% | - Use Ingress rules to expose applications - Provide and troubleshoot access to applications via services - Demonstrate basic understanding of NetworkPolicies |
Linux Foundation Certified Kubernetes Application Developer Sample Questions:
You are developing a Kubernetes application that requires dynamic configuration updates. You decide to utilize ConfigMaps to manage these configurations. You have a ConfigMap named 'app-config' containing the following configuration: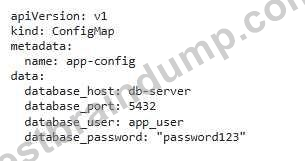
Your application retrieves these configuration values from the 'app-config' ConfigMap. You need to update the 'database_password' value without restarting the application pods. How can you achieve this?
Correct Answer:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
I). Update the ConfigMap:
- Create a new ConfigMap with the updated 'database_password' value.
- Replace "password123" with your new desired password.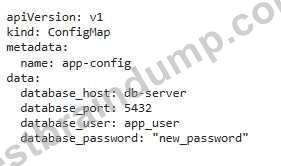
- Apply the updated ConfigMap using the following command: bash kubectl apply -f updated_app_config.yaml 2. Verify the Update: - Use the 'kubectl get configmap app-config -o yaml' command to verify that the 'database_password' value has been updated in the ConfigMap. 3. Application Reloads: - Ensure that your application is configured to watch for changes in the ContigMap and automatically reload the configuration when it detects an update. This behavior will depend on your application's code and how it interacts with Kubernetes. Common approaches involve: - Using a sidecar container that watches the ConfigMap for changes. - Integrating with tools like Kubernetes ConfigMap Reloader- This approach allows you to update the without restarting the application pods, minimizing downtime and ensuring a smooth transitiom ,
You're working on a Kubernetes application that involves retrieving data from a database. You have a Deployment With multiple pods, each accessing the database directly. To improve the application's performance and reliability, you want to implement an adapter pattern that introduces a service layer to handle database interactions. This layer should be responsible for connection pooling, caching, and error handling, making the application more resilient to database outages.
Reveal Solution Discussion 0Correct Answer:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Service Account:
- Create a service account for the application. This will be used by the service layer to access the database.
- Apply the service account to the cluster: 'kubectl apply -f db-setvice-account.yamr 2. Create a Role and Role8inding: - Create a role that grants tne necessary permissions to access the database.
- Create a role binding that associates the role with the service account
- Apply the role and role binding to the cluster: - 'kubectl apply -f db-access-role.yaml' - 'kubectl apply -f db-access-binding.yaml 3. Create the Service Layer Deployment: - Deploy the service layer component. This can be a containerized application that handles database interactions.
- Apply the deployment: 'kubectl apply -f db.-service-yaml 4. Create a Secret for Database Credentials: - Create a secret to store sensitive database credentials.
- Apply the secret 'kubectl apply -f db-credentials.yaml' 5. Create a Service for the Service Layer: - Create a service to expose the service layer to the application pods.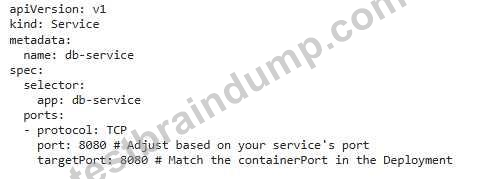
- Apply the service: 'kuoectl apply -f db-seMce.yaml' 6. Llpdate the Application Deployment: - Update the Deployment for your main application to use the service layer.
T Test and Verify' - Verify the changes: - Check the logs for both the service layer and the application. - Test your application's functionality. Note: - Ensure to replace placeholders like ''. ''. ''. ''. ''. ''. and with your actual values. - This is a basic example, and you may need to adjust the configuration based on your specific service layer and database implementation. ,
You have a microservice application that consists of two components: a web server (using Nginx) and a database (using PostgreSQL). The web server needs to access the database through a local connection, but due to network security restrictions, the web server cannot connect to the database directly. Describe how you can utilize a sidecar container to resolve this issue and ensure the database connection is secure.
Reveal Solution Discussion 0Correct Answer:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
1. Create a Sidecar Container:
- Define a new container in your Deployment's 'spec-template-spec-containers' array, alongside the existing Nginx container. This new container will house the necessary tools for facilitating a secure database connection.
- Name this container appropriately, for example, 'database-proxy'
- Choose an image that contains the required software for database connection, such as 'postgres' or 'postgresqr
- Use a sidecar pattern in the Deployment YAML file. You can specify the sidecar in the container array in the Pod specification:
2. Database Connection Configuration: - Configure the sidecar container to connect to the database. - Establish a connection using the database user credentials and connection string. - If you use a secure connection, ensure that the certificates and private keys are accessible to the sidecar container. 3. Communication Between Containers: - Configure your web server container to communicate with the sidecar container. - Use environment variables to specify the hostname and port of the sidecar container, enabling the web server to connect to the database proxy within the pod. 4. Volume Sharing: - Optionally, share a volume between the web server and the sidecar container to facilitate shared data access, such as database configuration files. 5. Deploy the Deployment: - Apply the updated Deployment YAML file to your Kubernetes cluster using 'kubectl apply -f my-app.yaml' 6. Test the Application: - Access your web server application and confirm that it successfully connects to the database through the sidecar container.
Context
You are asked to scale an existing application and expose it within your infrastructure.
First, update the Deployment nginx-deployment in the prod
namespace :
. to run 2 replicas of the Pod
. add the following label to the Pod :
role: webFrontEnd
Next, create a NodePort Service named rover in the prod namespace exposing the nginx-deployment Deployment 's Pods See the Explanation below for complete solution.
Correct Answer:
Below is an exam-style, step-by-step solution (commands + verification). Follow exactly on host ckad000.
0) Connect to the right host
ssh ckad000
(Optional but good sanity check)
kubectl config current-context
kubectl get ns
1) Inspect the existing Deployment (to know its labels/ports)
kubectl -n prod get deploy nginx-deployment
kubectl -n prod get deploy nginx-deployment -o wide
Check what labels the Pod template already has (important for the Service selector):
kubectl -n prod get deploy nginx-deployment -o jsonpath='{.spec.template.metadata.labels}{"\n"}' Check container ports (so we expose the correct targetPort):
kubectl -n prod get deploy nginx-deployment -o jsonpath='{.spec.template.spec.containers[0].ports}{"\n"}' If ports output is empty, it's still often nginx on 80, but the safest is to confirm by describing a pod later.
2) Update Deployment to 2 replicas
Fastest:
kubectl -n prod scale deploy nginx-deployment --replicas=2
Verify:
kubectl -n prod get deploy nginx-deployment
3) Add label role=webFrontEnd to the Pod (Pod template label)
You must add it under:
spec.template.metadata.labels
Use a patch (quick + safe):
kubectl -n prod patch deploy nginx-deployment \
-p '{"spec":{"template":{"metadata":{"labels":{"role":"webFrontEnd"}}}}}' Verify the Deployment template now includes it:
kubectl -n prod get deploy nginx-deployment -o jsonpath='{.spec.template.metadata.labels}{"\n"}' Now verify the running Pods have the label (important!):
kubectl -n prod get pods --show-labels
If the label doesn't show on pods immediately, wait for rollout:
kubectl -n prod rollout status deploy nginx-deployment
kubectl -n prod get pods --show-labels
4) Create a NodePort Service rover exposing the Deployment's Pods
4.1 Get a reliable target port
Try to read containerPort:
kubectl -n prod get deploy nginx-deployment -o jsonpath='{.spec.template.spec.containers[0].ports[0].
containerPort}{"\n"}'
* If this prints a number (commonly 80), use it as --target-port.
* If it prints nothing/empty, check a pod:
POD=$(kubectl -n prod get pod -l role=webFrontEnd -o jsonpath='{.items[0].metadata.name}') kubectl -n prod describe pod "$POD" | sed -n '/Containers:/,/Conditions:/p' | sed -n '/Ports:/,/Environment:/p' Assuming nginx is on 80 (most common), create the service:
kubectl -n prod expose deploy nginx-deployment \
--name=rover \
--type=NodePort \
--port=80 \
--target-port=80
If your nginx container port is different (e.g., 8080), change --target-port=8080 accordingly.
5) Verify Service + endpoints (critical)
kubectl -n prod get svc rover -o wide
kubectl -n prod describe svc rover
kubectl -n prod get endpoints rover -o wide
You should see 2 endpoints (matching 2 pods).
Also confirm the pods are Ready:
kubectl -n prod get pods -l role=webFrontEnd -o wide
Quick "CKAD checkpoints"
* Deployment in prod has replicas=2
* Pod template has label role=webFrontEnd
* Service rover in prod is NodePort
* Service endpoints point to the nginx pods
You have a Kubernetes cluster with a Deployment that runs a critical web application. The application's codebase is in a Git repository, and you want to automatically deploy a new version of the application whenever a new commit is pushed to the 'master branch ot the repository. You need to ensure that the deployment process iS seamless and doesn't result in downtime for the web application.
Reveal Solution Discussion 0Correct Answer:
See the solution below with Step by Step Explanation.
Explanation:
Solution (Step by Step) :
I). Set up a Git repository:
- Create a Git repository on a platform like GitHub, GitLab, or Bitbucket.
- Store your web application's code in this repository
2. Configure a webhook:
- Go to the settings of your Git repository and configure a webhook.
- The webhook URL should point to your Kubernetes clusters API server.
- Set the webhook event to 'push' and the branch to 'master
3. Create a Deployment
- Create a Deployment YAML file with the following configuration: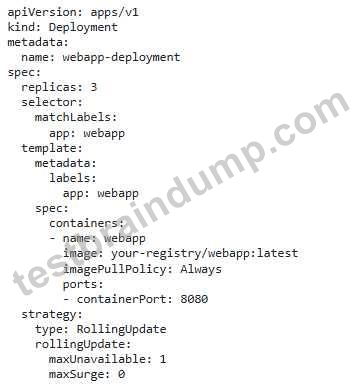
4. Create a Kubernetes Secret: - Store your Git repository's credentials in a Kubemetes secret - This secret will be used to authenticate the webhook request from your Git repository. 5. Create a Job: - Create a Job YAML file with the following configuration:
6. Apply the resources: - Apply the Deployment, Secret, and Job YAML files to your Kubernetes cluster 7. Test the deployment: - Push a new commit to the 'master' branch of your Git repository. - Observe that the Job runs and updates the Deployment with the new image. - VeriSi that the web application is still accessible during the update process.
Viewing page 1 out of 48 pages.
Viewing questions 1-5 out of 239 questions.
 Phoebe

 Lee
 Algernon
 Fitch
 Quentin

 Andrew

 George
 Jane
 Hobart
 Michell
 Arvin
 Maggie
 Justin
 Odelette
 Merle
 Geoff
 Montague
 Kerwin
 Quennel
 Jerome
 Cyril
 Vera